

Software quality is a critical factor in ensuring the performance and usability of applications. As businesses increasingly depend on software to manage operations, deliver services, and engage with customers, ensuring that applications function as expected has become essential. Even minor defects can lead to operational disruptions and security vulnerabilities.
With software applications becoming more complex and development cycles growing shorter, testing has become an integral part of the software development lifecycle. It enables teams to identify defects early, validate functional requirements, assess performance across different environments, and verify compliance with quality standards. A reliable software testing service can help businesses systematically evaluate application quality, minimize risks, and ensure that software meets both technical requirements and user expectations.
This article discusses the fundamentals of software testing, its importance, the processes involved, and the different testing approaches used to develop high-quality software.
What is Software Testing?
Software testing is a process used to ensure a software program performs as planned and is suitable for its intended purpose by testing various parts of a product to detect bugs, problems, or unexpected behavior before the software is released to users. Tests can be run at any point in the software development lifecycle rather than being considered the last step before release.
The purpose is not just to find bugs. Software testing is also a way to ensure that an application is stable, secure, usable, and can work under many settings. Depending on the product and its needs, testers may test anything from individual functionalities and user interactions to performance, ease of use, and level of security.
Testing can be done manually or with the help of automated technologies, or a combination of both. Different stages use different testing methodologies. This allows development teams to spot problems earlier, lower risks, and provide software that provides a more dependable experience for their users.
Why is Software Testing Important?
Software development is more than just making software. Testing helps teams understand if the product is actually working as it should, where issues may exist, and whether it is ready to give a stable experience to users. Here are some of the important benefits of software testing:
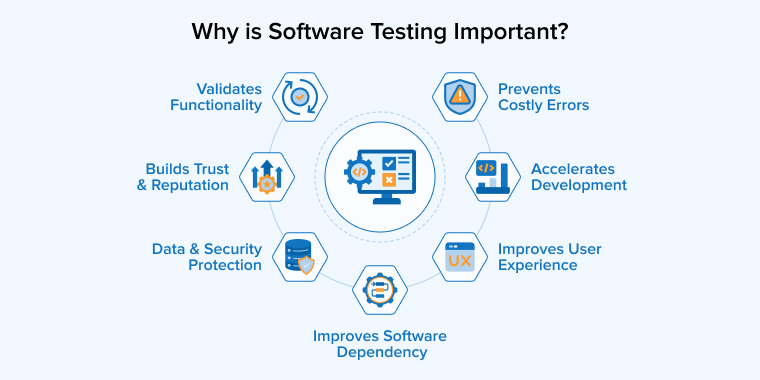
Prevents Costly Errors
Detecting errors early is often less expensive than correcting bugs after release. Testing allows teams to uncover issues before they reach the users, saving time and money on fixing them after release.
Improves Software Dependency
Users expect software to behave the same way in diverse contexts. Testing helps teams develop more reliable solutions by testing how an app performs in different scenarios.
Data and Security Protection
Security testing helps identify vulnerabilities that could expose sensitive data or allow unauthorized access to systems. Finding these issues before release allows teams to fix them before they become bigger problems.
Improves User Experience
A product may function correctly but still fail to deliver a satisfactory user experience. Testing also reveals usability difficulties, confusing interactions, and other aspects that can impact user satisfaction.
Validates Functionality
Testing validates that features work as required and expected. It verifies important features perform correctly before the software is delivered to users for better satisfaction.
Builds Trust and Reputation
Bugs and failures can quickly influence how people perceive a product and the company behind it. A solid and accurate testing of software leads to consistent experience and better confidence of users.
Accelerates Development
Testing gives teams valuable insight into their product’s quality and helps developers catch problems earlier in the development cycle. This leads to more informed judgments and releases with greater confidence.
Manual Testing VS Automated Testing
Testing can be approached in different ways depending on the software, testing goals, and stage of development. The two broad approaches are manual testing and automated testing. While both aim to identify errors and assess that software behaves as expected, they differ in how tests are performed, how quickly they can be repeated, and where they are most useful.
What Is Manual Testing?
The term “manual testing” refers to the process by which a tester verifies the software application without the use of automated scripts or tools. The tester replicates the user’s actions by entering data, clicking buttons, verifying outputs, and searching for unexpected behavior.
When specified automated tests fail to find issues, human observation and judgment can be invaluable in exploratory, usability, and ad hoc testing. Also, it might be a good choice for less common tests or smaller applications.
What Is Automated Testing?
In automated testing, test cases are executed automatically using scripts, testing frameworks, and specialized tools. Once configured, these tests require minimal manual intervention and are particularly useful for large applications and repetitive testing tasks.
For regression testing, where the same tests may need to be run every time the code changes, automation is very helpful. As an essential part of modern development and CI/CD processes, it has the potential to increase accuracy, decrease human error, and deliver feedback more quickly.
Manual Testing vs Automated Testing: Key Comparison
Automated testing is more efficient, consistent, and quick when tests need to be run multiple times, while manual testing is more flexible and relies on human judgment. Let’s take a look at the tabular comparison below to get a quick idea.
| Parameter | Automated Testing | Manual Testing |
|---|---|---|
| Speed | Faster once automation is set up | Generally slower for repetitive tests |
| Initial effort | Requires time to create and maintain scripts | Usually lower to get started |
| Human involvement | Low during test execution | High |
| Accuracy | More consistent for repeated tests | Can be affected by human error |
| Repeatability | Easy to run repeatedly | Time-consuming for repeated tests |
| Execution | Executed using scripts and tools | Performed manually by testers |
| Human judgment | Limited to what the test is programmed to check | Strong advantage |
| Best suited for | Repetitive and regression testing | Exploratory and usability testing |
Types of Software Testing
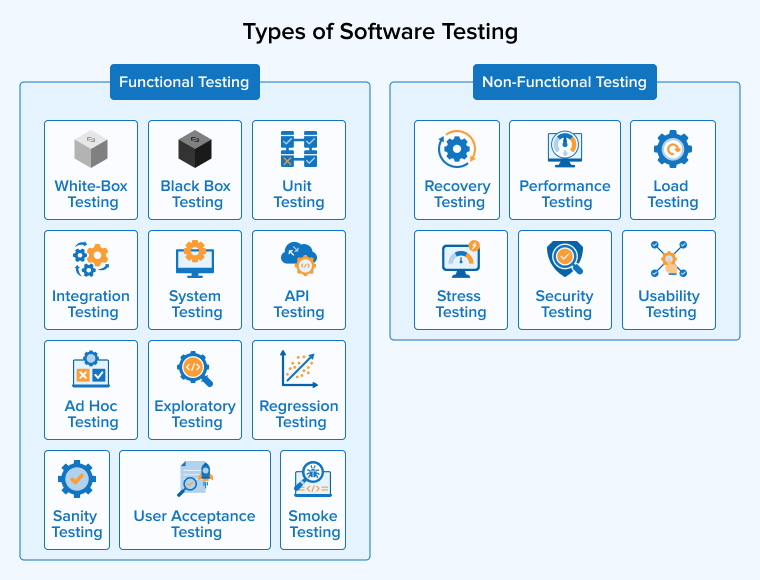
Software testing is more than simply testing that a specific feature works. Software testing is broadly categorized into functional and non-functional testing, with each category focusing on different aspects of the software’s behavior and performance.
Together, they help teams verify what the software does and how well it performs.
1. Functional Testing
Functional testing is the process of verifying whether the features and functions of a software program work according to the defined requirements. It addresses inputs, outputs, user interactions, business logic, and whether the program produces the intended results. For instance, functional testing of an online shopping app can verify that users can log in, add things to the cart, apply discounts, and make the payment successfully.
White-Box Testing
White-box testing tests the internal structure, logic, and code of an application. Testers or developers know the source code and use that understanding to check every path, condition, and function.
Black Box Testing
Black-box testing is done from a user perspective without looking at its internal code. Testers enter data and see the outputs. This helps them to understand whether the software works as per its requirements or not.
Unit Testing
Unit testing tests individual components or sections of code in isolation. It helps developers detect problems early by proving that a particular function, method, or module gives the expected result.
Integration Testing
Integration testing ensures that different modules or components work correctly when combined. It helps identify issues related to data exchange, interfaces, and communication among the various elements of a program.
System Testing
System testing evaluates the entire application as a single unit. It determines whether the integrated system meets the specified standards and whether its features and workflows function together properly.
API Testing
API testing verifies that application programming interfaces are working properly. It is concerned with requests and responses, manipulation of data, authentication, and communication between different software components.
Ad Hoc Testing
Ad hoc testing is an informal testing approach. It does not follow a predefined test strategy or set of test cases. Instead, testers test the application at their discretion, relying heavily on intuition and experience to identify unexpected problems quickly.
Exploratory Testing
In exploratory testing, learning, designing the test, and running the test are all done simultaneously. Testers do not follow pre-defined scenarios. They explore the application and adjust their approach based on what they find.
Regression Testing
Regression testing ensures that changes to the code, upgrades, or new features have not affected existing functionality. This is particularly useful for apps that get updated often.
Sanity Testing
Sanity testing is a quick check performed after minor changes or bug fixes. It confirms that the relevant functionality works as expected before the team proceeds with more rigorous testing.
Smoke Testing
Smoke testing is a quick check of a freshly built system to determine whether its most important features work well enough to proceed to the next stage of testing. This saves teams time by preventing them from testing an unstable build.
User Acceptance Testing
UAT (User Acceptance Testing) is a process of testing to verify that the software fits business requirements and the real-world needs of its target users. Usually, it’s done before the final release.
2. Non-Functional Testing
Non-functional testing evaluates a software application’s performance beyond its core functionality. While functional testing asks, “Does the software work?” non-functional testing asks, “How well does it work?” It assesses attributes such as speed, accuracy, usability, reliability, and stability under varying conditions. The purpose of non-functional testing is to ensure that the software not only works correctly but also provides users with a satisfactory experience.
Recovery Testing
Recovery testing assesses the ability of the software to recover from crashes, hardware failures, network failures, or system issues. It helps to verify if the application can recover data and resume normal functioning.
Performance Testing
Performance testing measures the responsiveness, stability, speed, and resource usage. It helps teams figure out whether the software can deliver an acceptable experience under the intended settings.
Load Testing
Load testing evaluates software performance under a predicted level of workload or user traffic. It helps determine whether the system can support typical demand without significant performance issues.
Stress Testing
Stress testing pushes an application beyond its normal operating capacity. This allows teams to see how the system performs under harsh situations and where its breaking point is.
Security Testing
The goal of security testing is to identify any vulnerabilities that would allow applications, systems, or sensitive information to be attacked or accessed illegally. It looks at things like authentication, authorization, and data privacy.
Usability Testing
Usability testing focuses on how simple and intuitive an application is for its users. It helps you spot confusing navigation, tough workflows, imprecise instructions, and other issues that can impair the overall user experience.
Compatibility Testing
Compatibility testing ensures the program functions well on multiple browsers, operating systems, devices, hardware configurations, and network conditions. This is very important for web and mobile apps.
Software Testing Methods
Software testing methods are classified based on how much testers know about the application’s internal code and architecture. The three main methods are black-box, white-box, and gray-box testing, each suited to different testing requirements.

1. Black-Box Testing
Black-box testing refers to the process of testing where the tester does not have any prior knowledge of the internal workings of the application. The tester has no understanding of the system architecture and no access to the source code. During a black-box test, a tester will often interact with the system’s user interface by providing inputs and examining outputs without understanding how or where the inputs and outputs came from.
Black-box testing is a strong testing approach as it tests the system end-to-end. In this type of testing, a tester can simulate user activity and see if the system delivers expected outcomes. The design of app development is to satisfy end users and their expectations to obtain an acceptable answer to their requests.
A black box test assesses all essential subsystems along the route, including the user interface/user experience, web server, and application.
Features of Black Box Testing
Software development processes aren’t complete without black-box testing because of the many advantages it provides. Among the most significant features of black box testing are:
- Emphasize External Behavior: By simulating real-world user actions and inputs, black box testing seeks to determine how well a program works from the user’s point of view.
- Independence from Internal Code: Black box testing is beneficial for testers without programming experience as it does not need to understand the internal code or implementation details. By avoiding access to the application’s source code, testers conducting black box testing can concentrate on the app’s external behavior and features effectively.
- Requirements-based Testing: To make sure the application satisfies the standards, black box testing is usually focused on the application’s needs.
- Different Testing Techniques: A wide variety of testing methodologies, including functional testing, usability testing, acceptability testing, and regression testing, can be employed to conduct black box testing.
- Identification of Interface-Level Bugs: For interface-level issues like missing functionality, inaccurate data processing, or misleading error messages, black box testing is important.
- User-Centric Testing: Black box testing guarantees that the program provides a good user experience by concentrating on the end-user perspective.
- Test Case Design Techniques: To make sure all possible scenarios are covered, black box testing uses a variety of test case design approaches such as state transition testing, decision table testing, boundary value analysis, and equivalence partitioning.
- Compatibility Testing: The program’s compatibility with various contexts, browsers, operating systems, and devices can be verified with compatibility testing.
- Test Automation Support: Automated testing is a feature of many black box testing solutions, which speeds up the execution of repetitive test cases and shortens the testing cycle.
Pros of Black-Box Testing
- It is considered one of the most optimal choices for doing functional testing.
- Black box testing facilitates the rapid creation of test scenarios.
- Facilitates the seamless execution of the application.
- Technical expertise is not required for the tester. It is crucial to conduct testing by adopting the perspective of the user and considering things from their viewpoint.
- Testing is possible after the development of the project/application is completed. Both the testers and developers operate autonomously without interfering with each other’s domain.
- It is more efficient for applications that are huge and complicated.
- Defects and inconsistencies can be detected during the initial phases of testing.
- The testing is impartial since the designer and tester do not collaborate.
Cons of Black-Box Testing
- In the absence of technical or programming expertise, there is a risk of overlooking potential conditions that need to be checked in the given scenario.
- Having a larger number of test inputs might be a time-consuming and tiring process.
- There is a high likelihood of obtaining no outcome at the end of a test.
- Due to the time-consuming nature of the task, the entire program might not be thoroughly tested.
- Within a certain timeframe, it is feasible to reduce the amount of testing and exclude the analysis of all potential inputs and their corresponding outputs.
- Attaining comprehensive test coverage is unattainable for extensive and intricate projects.
- Black box testing relies on specifications, which makes it extremely challenging to create test cases without them.
Tools to Perform Black Box Testing
Software testers can automate and manage the testing process with the help of various black box testing tools. You can utilize these tools to develop test cases, run them, record the results, and create reports.
Here are a few well-known black box testing tools:
- Selenium: For online applications, specifically, Selenium finds widespread usage in black box testing. Black box testing on web-based systems can be greatly enhanced with the help of Selenium, an open-source testing framework that automates the testing of web browsers.
Without gaining access to the application’s source code, it analyzes its functioning by interacting with web components on the user interface in a way that simulates actual user interactions. - Appium: Many mobile app UI automation tools depend on Appium, a black-box automated testing tool. This tool is open-source. You can integrate the Appium framework for both mobile and desktop, and it’s easy to tie it into your Selenium-based framework.
- Cypress: Cypress is available in several versions. Open source and free to use, Cypress Core does require a membership to access premium features like a dashboard. For Angular-based app test automation, Cypress is the preferred tool.
2. White-Box Testing
The next method of testing is white-box testing, which involves thorough analysis and examination of the code from the grassroots level, like core logic and structure. Its other names are glass testing or open-box testing. When a tester works under this method, they know and have a complete understanding of the internal workings of the code to conduct white-box testing on an application. The tester must examine the source code to determine which unit/chunk of code is acting abnormally.
In white-box testing, testers extensively examine the code and other internal components of the program. They determine all the valid and invalid inputs before comparing the outputs to the intended results and the testing criteria. The software tester examines the statements and conditions, as well as the code pathways and data flows, for hidden mistakes or defect-prone components.
Although you can use white-box testing at the unit level, its implications are most commonly seen in integration testing and regression testing. The approach allows testers to inspect pathways inside units for code flaws and other issues that might prevent the product from performing as expected. The performance of the app depends on strong integration with previously tested code, lowering the likelihood of issues later on.
Feature of White Box Testing
Below are some of the most significant features of White Box Testing:
- Analysis of Code Coverage: White box testing is useful for analyzing an application’s code coverage and finding untested parts of code.
- The Ability to Access the Code: White box testing allows for the testing of specific operations, processes, and modules inside an application by requiring access to its source code.
- Addressing Logical Errors: Infinite loops and improper conditional statements are examples of logical flaws that white box testing can potentially find.
- Integration Testing: Integration testing benefits from white box testing since it enables testers to confirm that the application’s various components are cooperating as intended.
- Performing Unit Tests: Unit testing, which entails checking the functionality of various components of code, also makes use of white-box testing.
- Code Optimization: By revealing performance issues, repeated code, and other areas that could benefit from improvement, white-box testing can assist in optimizing code.
- Security Testing: To find security flaws in the application’s code, white-box testing can be utilized for that purpose as well.
- Design Verification: The implementation of the software’s internal design is checked to make sure it matches the specified design documentation.
- Verify Code Accuracy: This check ensures that the code follows all the rules and requirements.
- Dead Code Determination: When the software is operating regularly, it discovers and removes any code that isn’t utilized.
Advantages of White Box Testing
- It ensures that the entire code is tested thoroughly. Thus, it enhances the level of specificity in your tests.
- Reducing data duplication, unnecessary coding lines, and mistakes improves your code. Therefore, it is a great tool for keeping up with code standards.
- When developing software, it is possible to begin this testing early on. This method of testing comes in two varieties: unit testing and integration testing.
- Selenium, Appium, TestNG, and other test automation technologies make this task easy to automate. Therefore, it’s a method that saves time.
Drawbacks of White Box Testing
- Since you need to know how everything works on the inside, it’s a difficult testing method. Therefore, it adds complexity to a huge system.
- Reusing the test cases is not an option. It is recommended to rewrite the code and modify the test cases regularly.
Tools to Perform White Box Testing
Below are some of the best white box testing open-source tools:
- Veracode: Finding and fixing software bugs has never been easier or more cost-effective than using Veracode’s white box testing tools. You can utilize it to check the safety of desktop, online, and mobile apps, and it supports several programming languages.
- Bugzilla: One well-known tool for keeping track of bugs is Bugzilla. Assigning, managing, confirming, and resolving bugs are all part of their life cycle, and this tool lets you keep track of all these activities. Developers will have all the details they require to fix the issue if they track the actions that lead up to reproducing it.
- NUnit: When it comes to evaluating test results, the user-friendly and open-source NUnit framework does not need any human involvement. You can use it with any .NET language. It is compatible with NUnit’s parallel testing capabilities and data-driven tests as well.
3. Grey-Box Testing
Grey-box testing is a method of testing an application with only a basic understanding of its internal workings. The grey-box method is a process of testing that uses a simple black-box methodology to test complicated systems, allowing almost anybody to complete the tests, from developers to testers to end-users.
However, to build test cases, an engineer must have a working understanding of the software’s internal structure, which includes documentation on data structures, architecture, and functional requirements. In contrast to black-box testing, where the tester only evaluates the application’s user interface, grey-box testing allows the tester to access design papers.
Penetration testing, end-to-end system testing, and integration testing are all typical uses for grey box testing. Interactive Security Testing tools can also be used to do grey box testing. In these IAST tools, we can use a combination of white box testing to assess static code and tools used for black box testing when combined in IAST tools. These tools will enable developers to test effectively and apply maximum coverage to its aspects.
Features of Grey Box Testing
Here are the main features of gray box testing:
- Comprehending the fundamental technology and architecture of an application.
- Recognizing issues that arise in certain settings.
- Integrating automated and manual testing approaches.
- Acknowledging challenges that are both technical and practical.
Advantages of Grey Box Testing
- Testing is conducted with well-defined objectives for both users and developers.
- The majority of grey box testing is conducted from the user’s point of view.
- For this testing, strong programming abilities are not necessary.
- Gray box testing is non-intrusive.
- With gray box testing, developers get more time to resolve bugs.
- Gray box testing combines the best features of black box and white box testing.
- Testing in a gray box is objective. This helps minimize disagreements between developers and testers.
- Integration testing benefits greatly from gray box testing.
Drawbacks of Gray Box Testing
- It is challenging to identify errors while checking distributed systems using gray box testing.
- When code path navigation is hampered, it’s because the internal structure is not easily accessible.
- It is not possible to conduct thorough gray box testing without access to the source code.
- Algorithm testing is not a good fit for gray box testing.
- It is challenging to design the majority of the test scenarios.
Tools to Perform Grey Box Testing
Let’s take a look at the best Grey Box testing tools:
- Chrome Dev Tools: The vast majority of all online browser traffic originates from Google Chrome. Hence, utilizing the user-friendly features provided by Google for your application is a wise decision. It makes working on browser-based apps possible and is the preferred method for testing web writing and fixing layout errors. Grey Box Testing and debugging tools are available in Google Chrome. It makes the code more compatible with Chrome.
- JUnit: As an open-source framework, JUnit is restricted to the Java language while allowing users to conduct repeated tests. Although this limitation isn’t problematic on its own, it could be difficult for less experienced testers due to the complicated API and UI.
- PostMan: An easy-to-use testing tool for creating and interacting with HTTP APIs, Postman is available as a Google Chrome extension. One of its standout features is the ability to use the JavaScript library to build collections of requests.
Software Testing Life Cycle
The software testing life cycle (STLC) is a process that includes various activities that every software testing team must perform to ensure the software’s quality. There is a series of activities that must be conducted to perform software testing. It also specifies the type of test activities to be carried out and when would be the outcome of these test activities.
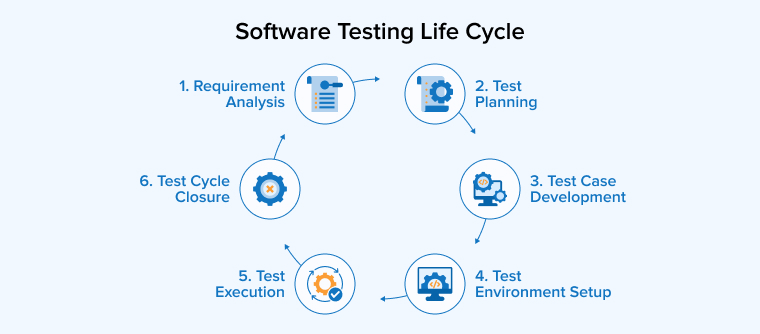
The STLC process comes with different activities, and each activity of this lifecycle must be carried out in a planned manner to get the perfectly secured software. Here are the different software testing life cycle phases –
1. Requirement Analysis
The first step is to do a requirement Analysis. The quality assurance team must understand the requirements of the software and figure out what to test & what the testing requirements will be.
2. Test Planning
The next step in the software testing life cycle is test planning. Here, all the software testing strategies are specified. This step is also popularly known as the Test Strategy phase. Here, the test manager gets involved and specifies the testing efforts and cost required for the project.
3. Test Case Development
After the test planning phase, the test case development process starts. Here, the testing department documents the detailed test cases and also prepares the test data. Once the test cases are ready, they are reviewed by the quality assurance lead.
4. Test Environment Setup
The next step is to set up an environment for tests. Here, the team makes sure that they have the right testing environment, which includes setting up hardware and software for testing.
5. Test Execution
After the testing environment is ready, the next thing to do is test execution. In this process, the testers execute the code and compare the generated results with the expected results. The analysis of the results starts from the very beginning of the execution process, and the test scripts are created throughout this process.
6. Test Cycle Closure
The final stage in the software testing life cycle is to close the test cycle. This process includes calling out the team members of the testing team and evaluating the entire cycle as per the quality cost, test coverage, time, and more.
Software Testing Best Practices
Successful testing is more than simply running as many test cases as you can. It’s about creating a testing process that is consistent, focused, and beneficial across the development lifecycle. The appropriate strategy can help teams discover problems early, minimize unnecessary rework, and keep the quality of the application as it develops. There are some best practices that can help you make your testing process more productive.
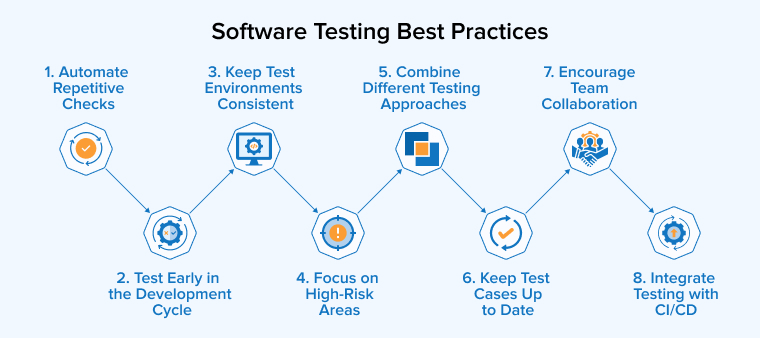
1. Automate Repetitive Checks
Automation works best for tests that need to be run repeatedly, such as regression and high-volume testing. Meanwhile, tests that rely on human judgment, like usability and exploratory testing, are frequently best done manually.
2. Test Early in the Development Cycle
Testing should not be left to the end of development. Testing earlier in the process allows teams to discover problems when they are easier and less costly to resolve, resulting in a smoother development process.
3. Keep Test Environments Consistent
A suitable test environment should closely replicate the production environment with relevant software, hardware, databases, and network configurations. This makes the test results more predictive of what users may encounter in real life.
4. Focus on High-Risk Areas
There is a difference in how important each test case is. Concentrate your testing efforts on the features that matter most, the ones that are used most often, and the ones where a failure will affect users or the business the most.
5. Combine Different Testing Approaches
Relying on a single testing approach can leave significant gaps. Broader coverage can be achieved by a balanced approach that includes unit, integration, system, acceptance, performance, security, usability, and other applicable tests.
6. Keep Test Cases Up to Date
Since software is always changing, tests can quickly become useless. Test cases should be reviewed often and updated to reflect changes in features, requirements, processes, or user expectations.
7. Encourage Team Collaboration
Testing is more effective when developers, testers, product teams, and other stakeholders communicate with each other frequently. Giving feedback and talking about requirements early helps teams see risks and handle issues before they become bigger problems.
8. Integrate Testing With CI/CD
Teams can test code changes anytime during development, not only at the end, thanks to automated tests and CI/CD pipelines. This gives faster feedback and helps teams catch problems quickly after they are implemented.
Summary
Software testing is an important part of developing software that people can trust and rely on. It’s more than just detecting issues before a product is released. An effective testing strategy helps teams understand application behavior, detect risks early, maintain user satisfaction, and ensure the product continues to work as it evolves.
Testing can take numerous forms, from functional and non-functional testing to black-box, white-box, and gray-box approaches. Manual and automated testing each have their place, with their own merits based on the conditions. The most important thing is not to depend on a single approach, but to mix the proper techniques, according to the product, users, and business requirements.
FAQ
QA (Quality Assurance) is a broader process to improve the whole software development process and decrease the chance of quality problems. Software testing is a QA activity that involves analyzing the product to discover errors and checking that it functions as intended.
Black-box testing, white-box testing, and gray-box testing are common methodologies for software testing. Depending on the testing objective, teams may also adopt methods such as functional, non-functional, exploratory, regression, usability, performance, and security testing.
Automation allows teams to execute repetitive tests faster, more consistently, and with less manual effort. With more frequent software releases, automated testing provides development teams with speedier feedback and the ability to detect errors sooner in the software development lifecycle.
A bug is a mistake or unexpected behavior in software that leads to an incorrect result. Usually, a defect is a flaw or difference from the intended requirement, and the two phrases are commonly used interchangeably in software testing.
Software Testers test apps to see if they fulfill requirements and perform as expected. Testers design and run test cases, record and track issues, do different kinds of testing, and interact with developers to address software glitches.
Software testing is categorized into major types such as functional testing and non-functional testing. Functional testing verifies that functions are working as expected, and non-functional testing looks at things like performance, security, usability, reliability, and compatibility.
Itesh Sharma is core member of Sales Department at TatvaSoft. He has got more than 6 years of experience in handling the task related to Customer Management and Project Management. Apart from his profession he also has keen interest in sharing the insight on different methodologies of software development.


Comments
Leave a message...